Compliance
Everything you set up in the onboarding journey feeds your compliance posture: the systems you connected and the findings they produce are mapped to ISM controls, tracked for readiness, and packaged for IRAP assessment with evidence-backed control statuses.
Frameworks
Compliance → Frameworks shows the frameworks you are tracking, with certification status and readiness against each. Open one to see its tabs: Controls, Essential Eight (for the ISM), Readiness, SOA and Target.
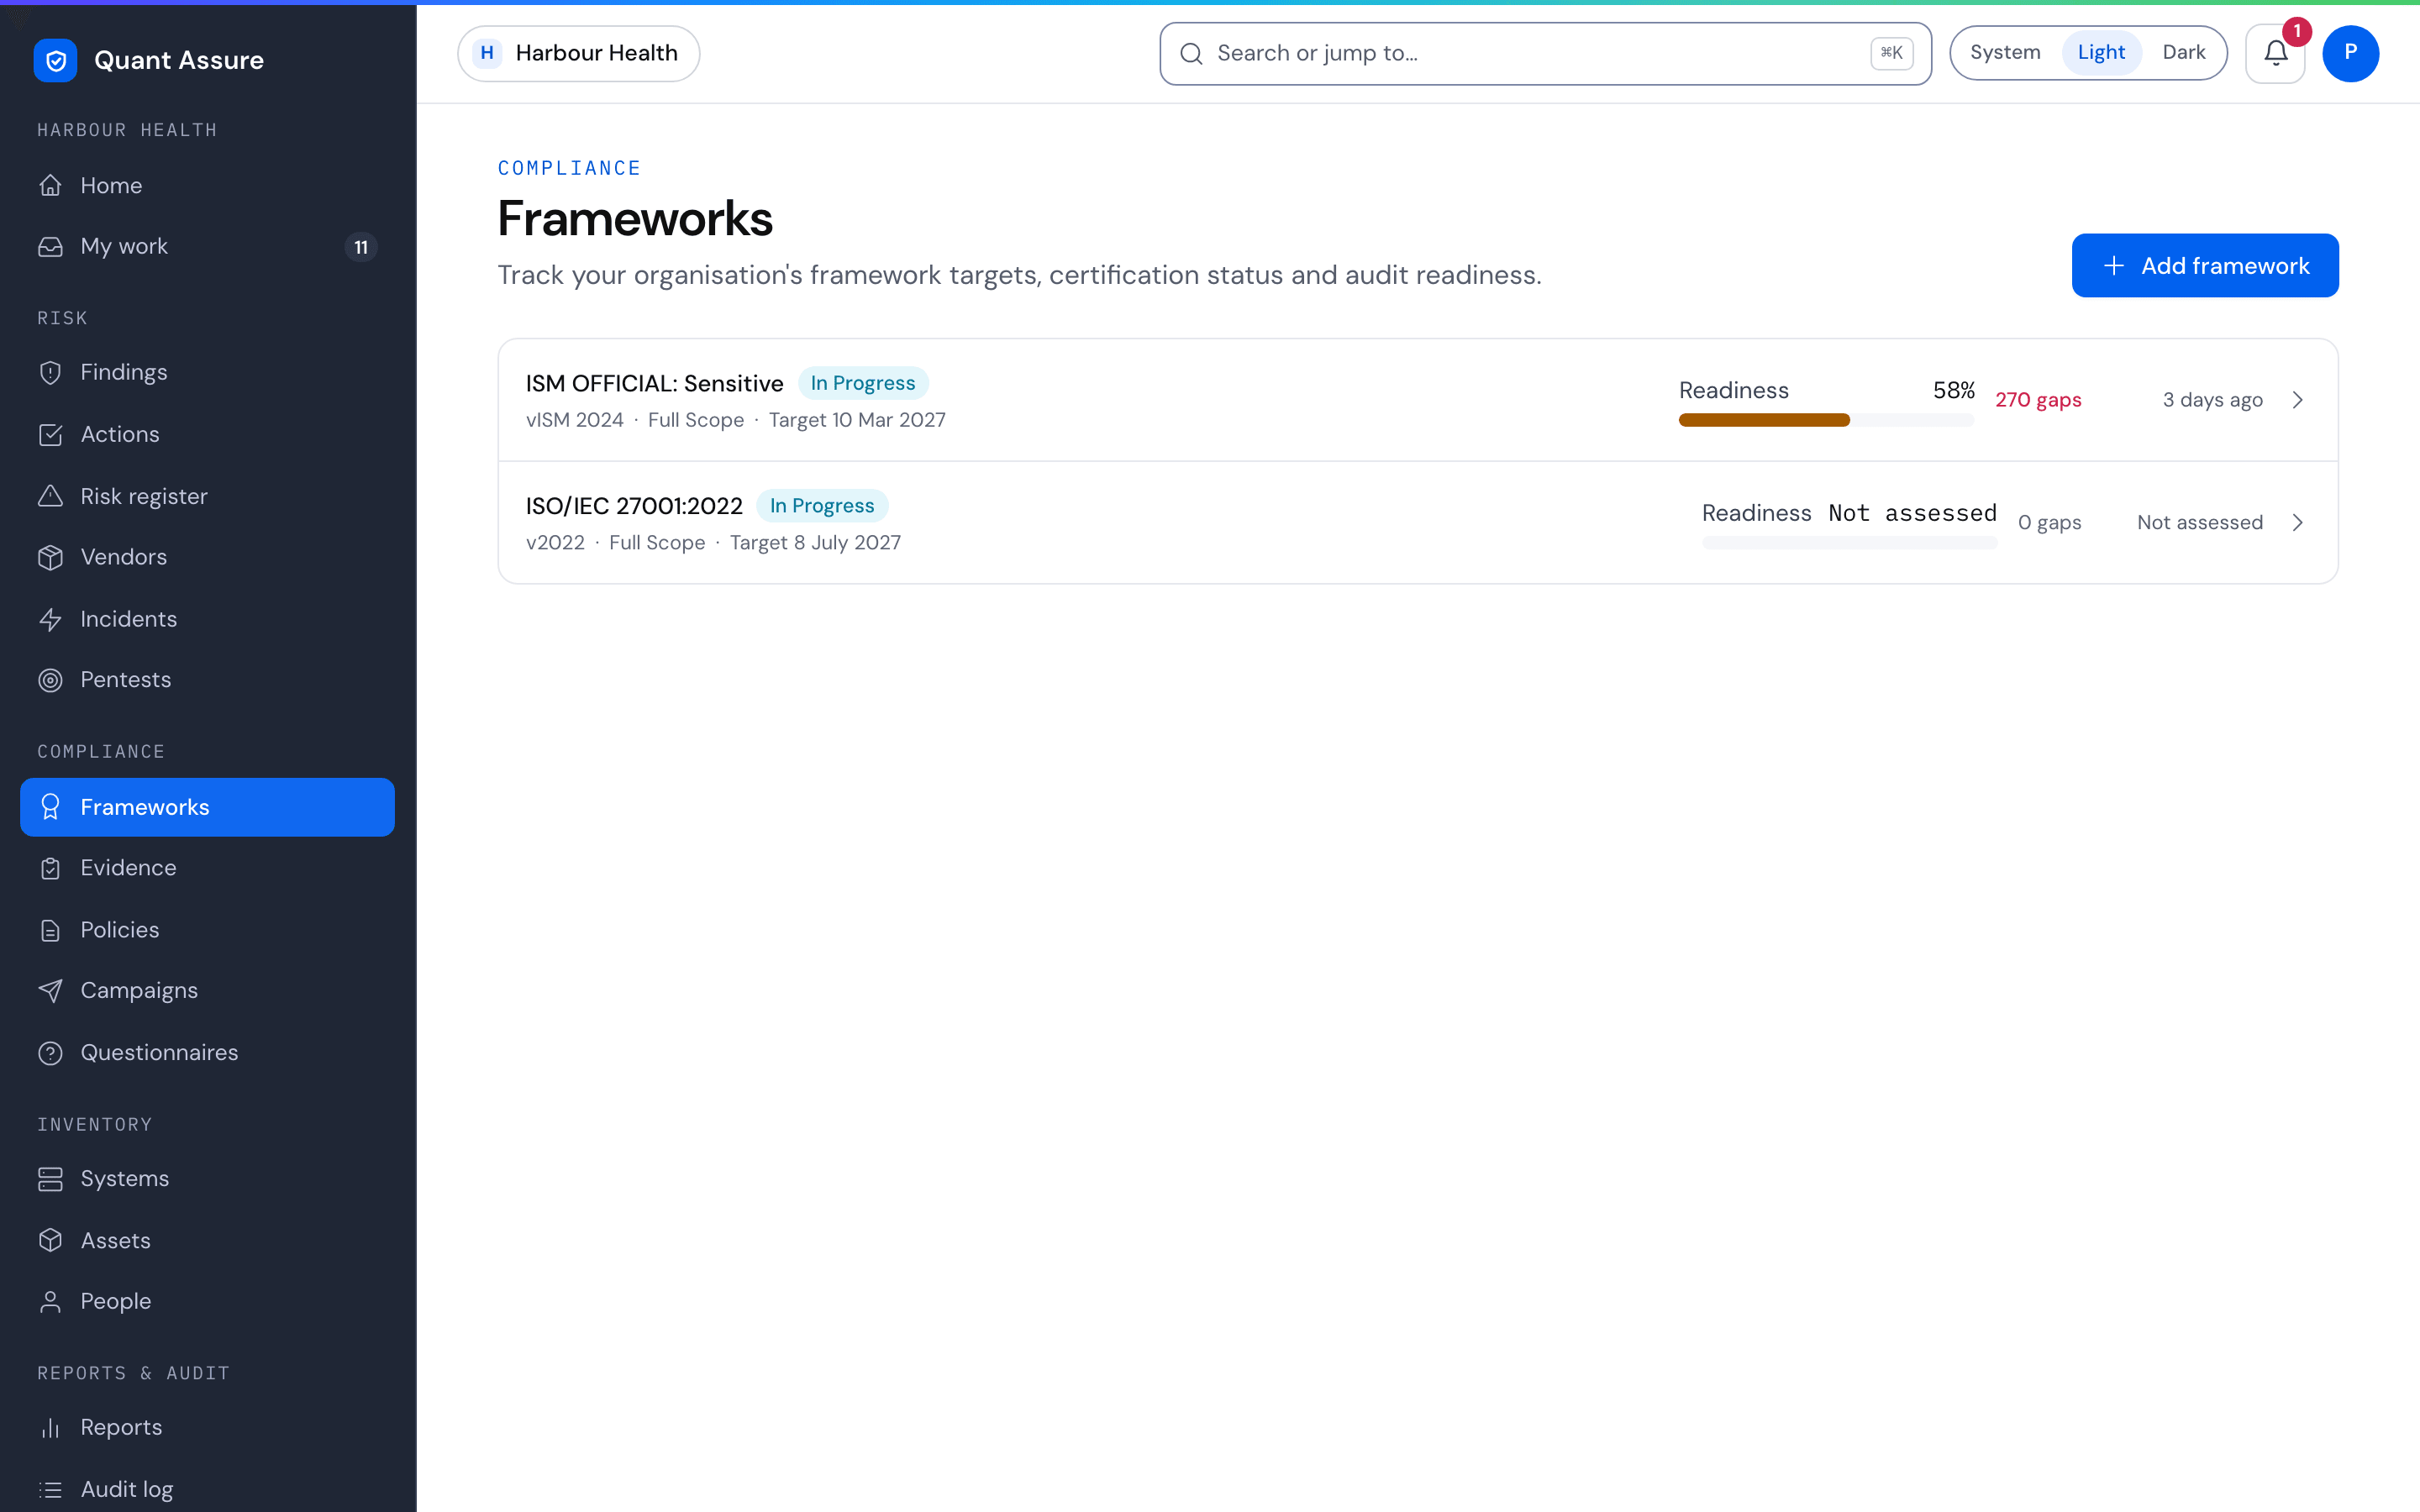
QuantAssure ships with the Australian Government ISM control catalogue (more than 1,000 controls in the current release), Essential Eight maturity tracking, and IRAP-oriented tooling. Controls carry per-org status (applicability, compliance state) and link to evidence: findings, resolutions, policies, and scan activity collected by your runs — so control status is backed by artefacts, not assertions.
ISM & IRAP
For agencies and suppliers facing IRAP assessment, QuantAssure maintains ISM control statuses with AI-assisted applicability assessment and links each control to the evidence your runs collect continuously. Findings from connectors arrive pre-mapped to ISM controls where the source event implies one (e.g. CloudTrail "logging stopped" → ISM logging controls). The Statement of Applicability report and compliance reports package this for your assessor.
New to IRAP or the ISM? The IRAP compliance guide and ISM controls guide cover the background; this section documents the product workflow.
How It Works
The compliance workflow has four phases:
- Connect — Set up systems with integrations to collect security data (learn more)
- Assess — AI maps findings to ISM controls and suggests compliance status
- Evidence — Automated and manual evidence is collected against controls
- Readiness — Track your compliance posture and generate your SOA report for assessors
Setting Up a Compliance Target
- Go to Compliance → Frameworks and click Add framework. The button appears only while there is a framework you have not added yet, and only for people who can edit.
- Select your framework (e.g., ISM OFFICIAL: Sensitive, the control set IRAP assessors test against)
- Choose a status (In Progress or Already Achieved) and set the target certification date
- Choose the scope (Full organisation or Partial Scope) and add scope notes
- Optionally enter the next audit date and the auditor or certification body, then click Add Compliance Target
What's Automated vs Manual
| Automated | Manual |
|---|---|
| Findings from pipeline scans | Implementation notes per control |
| Policy sync from Google Drive | Evidence for physical/procedural controls |
| AI compliance status suggestions | Applicability determinations |
| Asset inventory from integrations | Custom evidence uploads |
| Finding-to-control mapping | Assessor review via SOA import |
System Boundaries
- Evidence is scoped to registered systems and assets
- Register all systems in scope for your assessment
- Configure integrations for each system
- Run scans regularly to keep evidence fresh
- Assets not registered won't have automated evidence
Learn more about asset registration
Guides in This Section
- ISM Controls — Browse and manage ISM controls
- Evidence Collection — Automated and manual evidence
- Statement of Applicability — Report and import workflow for assessors
- Readiness Dashboard — Monitor compliance readiness
- Essential Eight — Maturity assessment
- Asset Registration — Register and classify assets